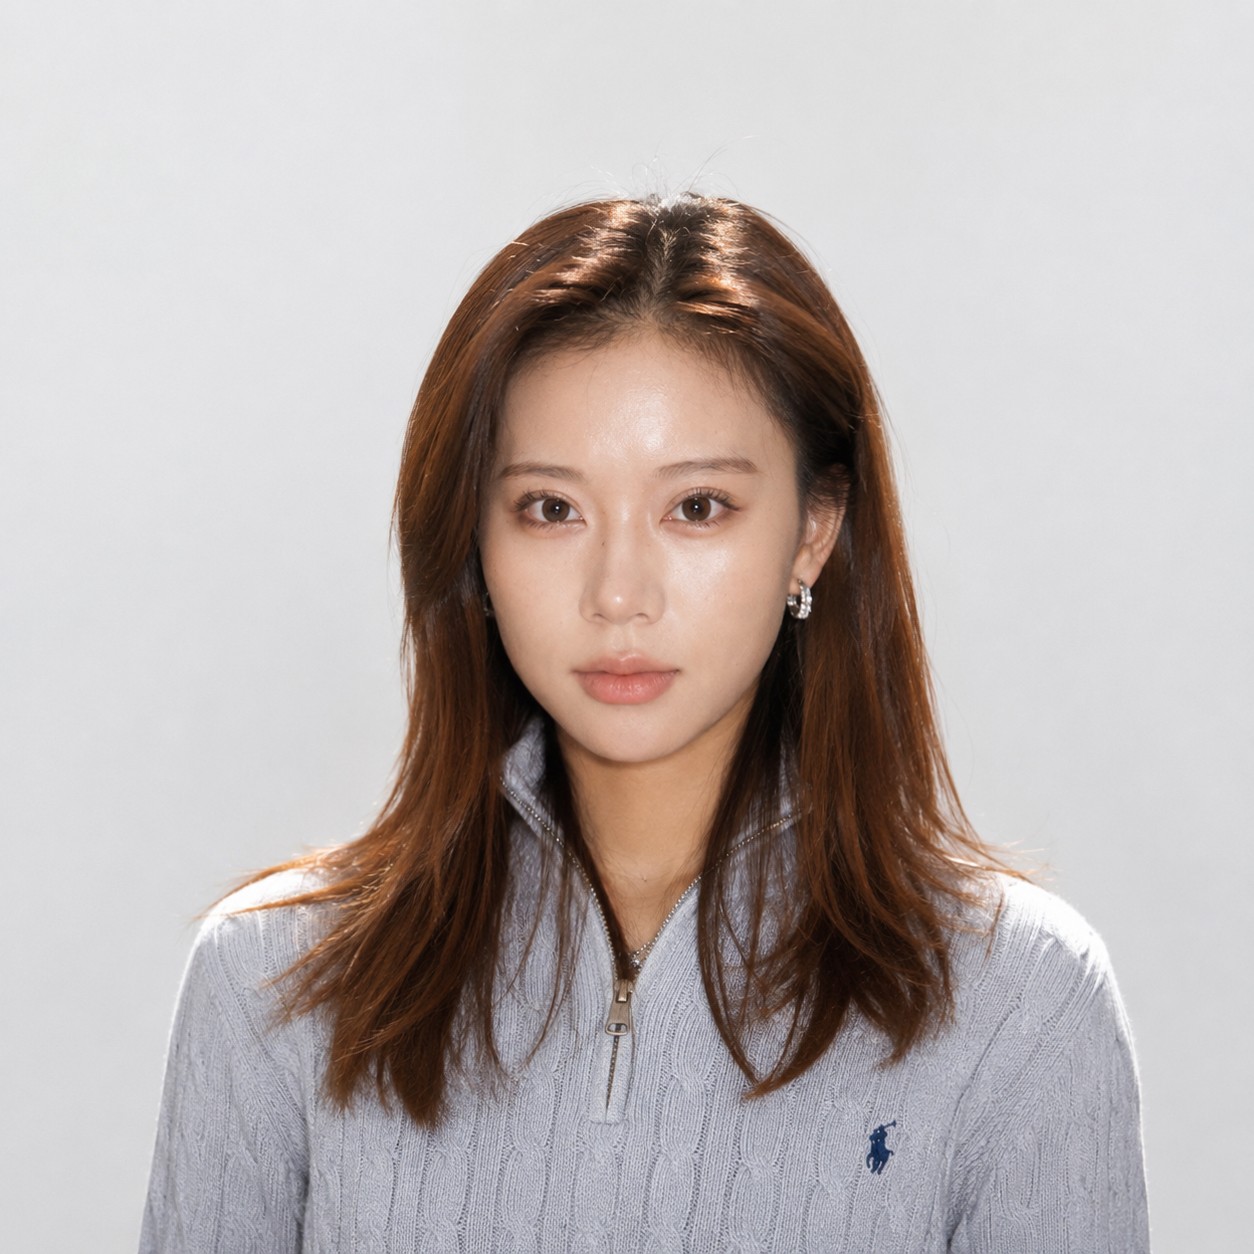
I am a Ph.D. student in Computer Science at Johns Hopkins University, co-advised by Prof. Yinzhi Cao and Prof. Ziyang Li. My research focuses on AI Security and Web Security, particularly the security of agentic systems, vulnerability discovery, and large-scale security measurement and evaluation.
Before transitioning to the Ph.D. program, I was a Master of Science student in Security Informatics at Johns Hopkins University, where I was fortunate to be advised by Prof. Yinzhi Cao, which sparked my research interest in web security. I earned my bachelor's degree in Computer Science from East China Normal University, where I graduated as an Outstanding Graduate. In Summer 2025, I was a Research Assistant at the University of Texas at Dallas under the supervision of Prof. Wei Yang, where I was fortunate to gain hands-on exposure to AI security research.
News
Looking forward to USENIX Security Symposium 2026 — see you there!
I'll present our Host Name Poisoning work at IEEE S&P '26 in San Francisco — see you there!
I'll join the academia track panel at the WiCyS Alumni Cybersecurity Panel — see you there!
Jayl-Break was named among ten teams in the Amazon Nova AI Challenge 2026, with a $250,000 grant to develop AI-assisted penetration testing for modern web applications. I am a core member of the team.
Publications
Poisoned by the Host: Large-Scale Measurement of Host Name Poisoning in Web Applications
Accepted: 47th IEEE Symposium on Security and Privacy (IEEE S&P 2026) · First AuthorPaper
Built a large-scale measurement pipeline to identify Host Name Poisoning vulnerabilities in real-world web applications.
VulDock: A Reproducible Benchmark for Agentic Vulnerability Exploitation
In preparation: International Conference on Learning Representations (ICLR 2027) · First Author
Agentic security benchmark with Dockerized CVEs, exploit oracles, and white-/grey-/black-box settings.
SoK: When Safe Agents Fail Together: The Security of Multi-Agent LLM Systems
Submitted: USENIX Security Symposium 2027 · First Author
SoK of attack surfaces, threat models, and defenses for multi-agent LLM systems.
When Localhost Is Not a Boundary: Browser-Driven Attacks on Local MCP Plugins
In preparation: USENIX Security Symposium 2027 · First Author
Browser-to-localhost attack study on MCP plugins and unauthorized local tool access.
Same Request, Different Boundary: Evaluating Cybersecurity Assistance across Conversational Contexts
Submitted: ACL Rolling Review · First Author
Introduces 3R-Bench to evaluate how conversational context changes cybersecurity assistance and refusal behavior.
BELUGA: Detecting and Exploiting E-commerce Logic Vulnerabilities via Semantics-aware, White-box Fuzzing
Submitted: 49th IEEE/ACM International Conference on Software Engineering (ICSE 2027) · Second Author
White-box fuzzing for semantic e-commerce logic vulnerabilities and exploit validation.
Mystra: Declarative Dynamic Taint Analysis via Shadow Virtual Machine
Submitted: 49th IEEE/ACM International Conference on Software Engineering (ICSE 2027) · Third Author
Declarative dynamic taint analysis for precise vulnerability tracking.
CVEs
Discovered and responsibly disclosed vulnerabilities resulting in 139 CVE assignments across real-world open-source software, including 87 Host Name Poisoning and 18 access control and authorization vulnerabilities, with 34 additional CVEs spanning authentication and session security, remote code execution, command injection, SSRF, path traversal, SQL and NoSQL injection, XSS, CSRF, information disclosure, credential exposure, and mass assignment.
Many of these findings are connected to papers currently under review and ongoing research projects and therefore are not yet public. CVE IDs were assigned through coordinated vulnerability disclosure, and technical details will be released as disclosure processes complete. A growing subset of the Host Name Poisoning findings has already been patched and publicly disclosed.
Host Name Poisoning · 87
Access Control and Authorization · 18
Other Web Security · 34
Research
Undergraduate Research
Xing Lian Technology: Blockchain Project, East China Normal University
Team Leader (Aug. 2022 – Aug. 2023)
Dual-chain blockchain architecture and threshold-signature authorization for secure, decentralized data exchange.
Won the University Student Innovation Award in the 2nd Yangtze River Delta FinTech Global Competition and the Gold Prize of "Challenge Cup" National College Student Entrepreneurship Plan Competition.
Experience
Teaching Assistant, EN.601.640 - Web Security, Johns Hopkins University | Instructor: Prof. Yinzhi Cao
Course Assistant, EN.601.640 - Web Security, Johns Hopkins University | Instructor: Prof. Yinzhi Cao
Summer Research Assistant, University of Texas at Dallas | Advisor: Prof. Wei Yang
Web & LLM Security Intern, Medivoice, Baltimore | Internship
Java Full-Stack Developer Intern, Capgemini, Shanghai | Internship
Talks
WiCyS Alumni Cybersecurity Panel
Panelist, academia track · Johns Hopkins WiCyS · April 17, 2026
Professional Services
External Reviewer
- IEEE Symposium on Security and Privacy (S&P '26)
- USENIX Security Symposium (Usenix '26)
- The ACM Conference on Computer and Communications Security (CCS '26)
- Network and Distributed System Security Symposium (NDSS '27)
Awards and Honors
Outstanding Graduate, East China Normal University (Top 10%)
First Prize, Shanghai Female College Student Innovation and Entrepreneurship Competition (Top 0.75%)
Scholarship, Academic Excellence jointly offered by Nezha Technology Co., Ltd. & ECNU (Top 2%)
Social Practice Outstanding Individual, East China Normal University (Top 0.6%)
Scholarship, Academic Excellence jointly offered by People's Financial Holdings Group & ECNU (Top 1%)
About Me
When I'm not hunting for vulnerabilities or buried in code, you'll probably find me at a table tennis court or sitting in front of a Go (围棋) board. I'm a 5 dan (五段) Go player, and the game has fundamentally shaped how I think. It teaches patience, long-term strategy, and how to spot patterns hidden in complexity, skills that turn out to be surprisingly useful in security research (probably).
I thrive in collaborative environments and believe the best ideas rarely come from working alone. Some of my favorite moments are brainstorming attack paths with teammates or walking through defense strategies with mentors. Those conversations often spark insights that would be hard to reach solo.
Outside of research, I love traveling and exploring new places. If you want to chat about table tennis, Go, or just share travel stories, feel free to message me on Instagram at brooke_yang_. You'll find plenty of travel photos there, probably more than I should admit.